vulnerability
Blog post
Hacking on Autopilot: Inside ARTEX Cybercrime Campaigns
Source: Check Point Research · Published · Last checked 2 hours ago · 1 min read
Publisher excerpt From Check Point Research
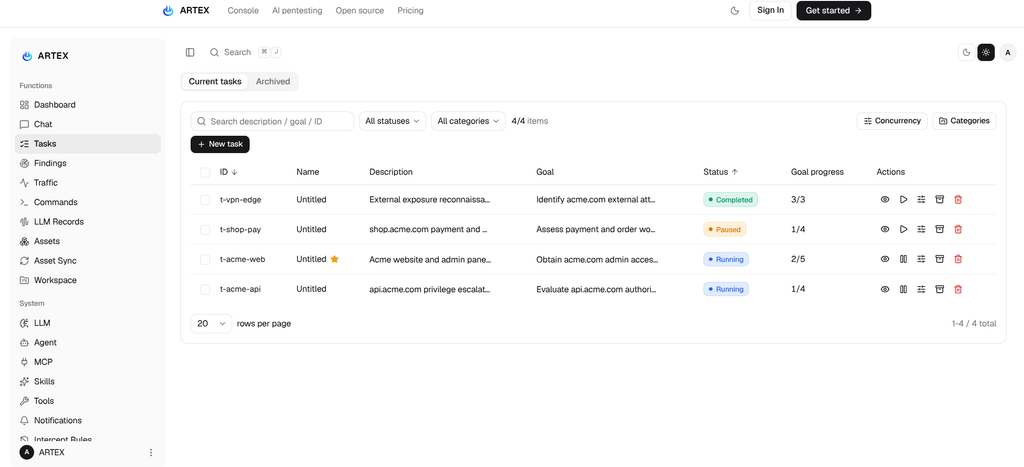
Key Points Introduction ARTEX is a Chinese open-source, AI-powered penetration testing platform designed to help security teams assess systems they own or are authorized to test. It uses large language models (LLMs) to coordinate multiple AI agents that plan tests, run security tools, and record evidence of potential vulnerabilities. Its web dashboard brings together assets, […] The post Hacking on Autopilot: Inside ARTEX Cybercrime Campaigns appeared first on Check Point Research.
Excerpt only, shown with attribution. This content belongs to the original publisher and has not been independently verified by CyberSecurity.pk.
More images