

vulnerability
Blog post
How to Find, Mitigate, and Patch the Critical Java4Shell Flaw (CVE-2026-114938) Now
Source: Qualys Security Blog · Published · Last checked 1 hour ago · 1 min read
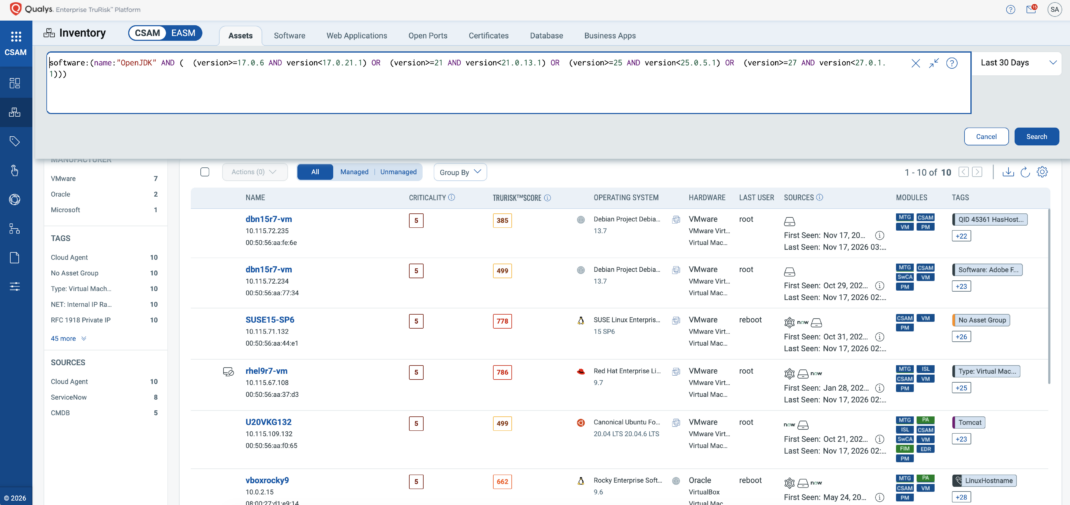
Publisher excerpt From Qualys Security Blog
Executive Summary Java4Shell (CVE-2026-114938) is a critical memory-corruption vulnerability in OpenJDK’s Base64 decoder. The researchers who found it rate it 9.2 under CVSS v4.0, and Oracle rates it 8.1 under CVSS v3.1. An attacker with no credentials can corrupt Java heap memory, read secrets from it, and reach remote code execution. Researchers demonstrated pre-authentication RCE […]
Excerpt only, shown with attribution. This content belongs to the original publisher and has not been independently verified by CyberSecurity.pk.
Related CVEs
Keywords: vulnerabilityrceremote code executionjava flawjava4shellCVE-2026-114938vulnerability newsQualys Security Blogcybersecurity newssecurity news Pakistan
Reference: Qualys Security Blog — blog.qualys.com ↗