

vulnerability
Imported story
Inside KeyDrift: Analyzing historical UAT-11473 activity on Cisco SD-WAN
Source: Cisco Talos Intelligence · Published · Last checked 1 hour ago ·
Publisher excerpt From Cisco Talos Intelligence
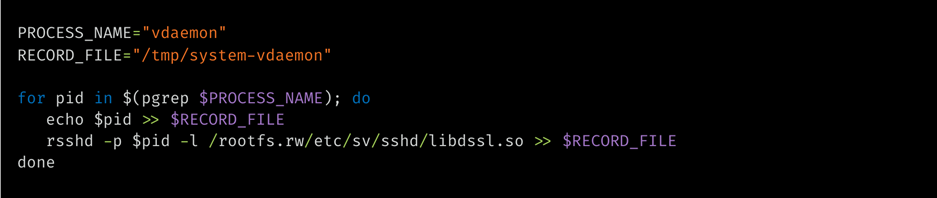
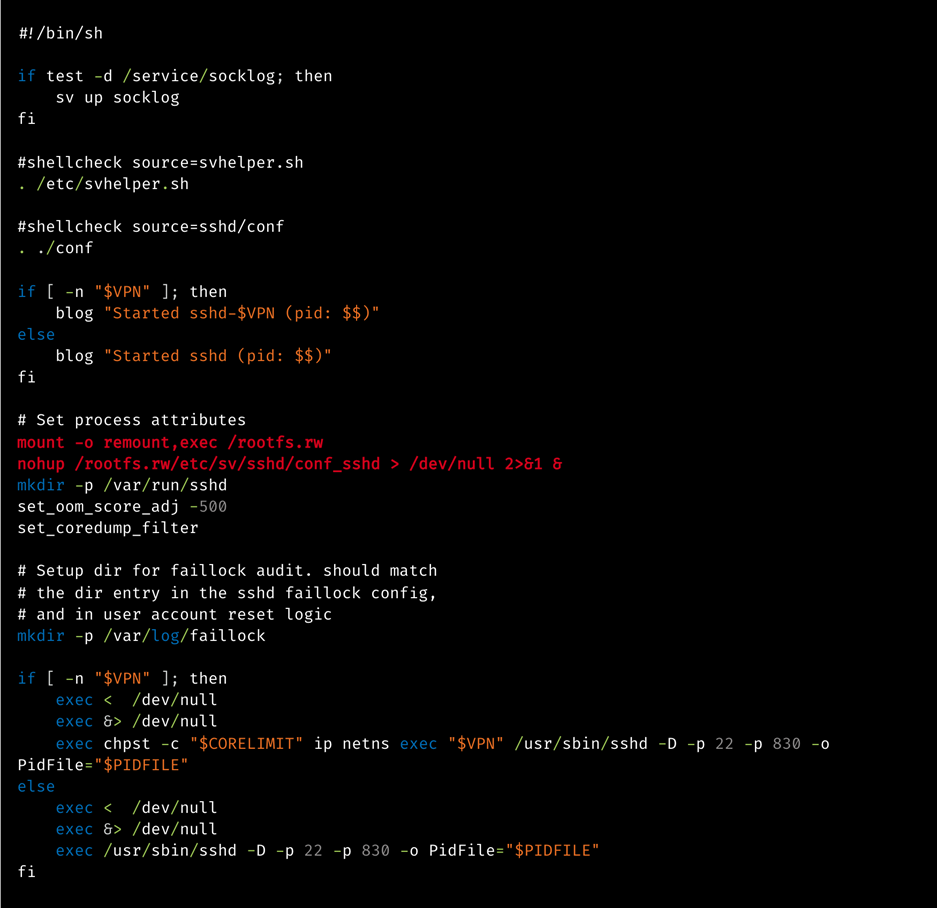
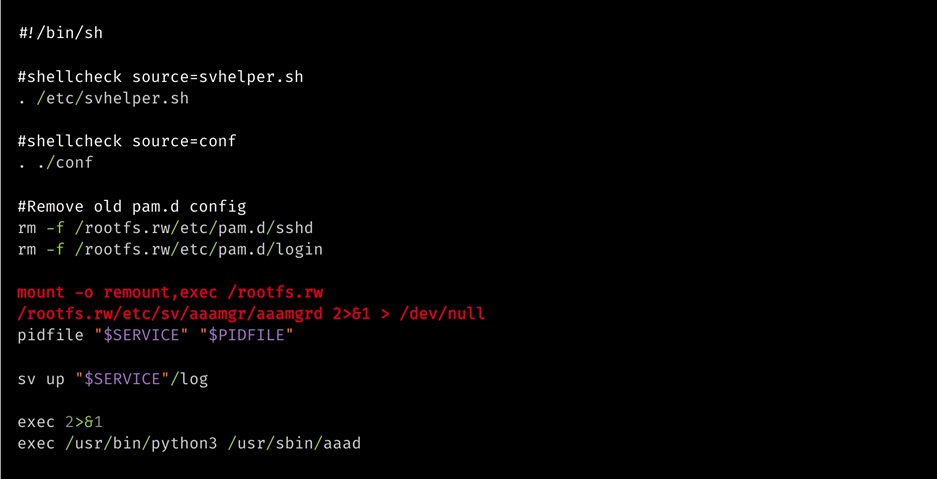
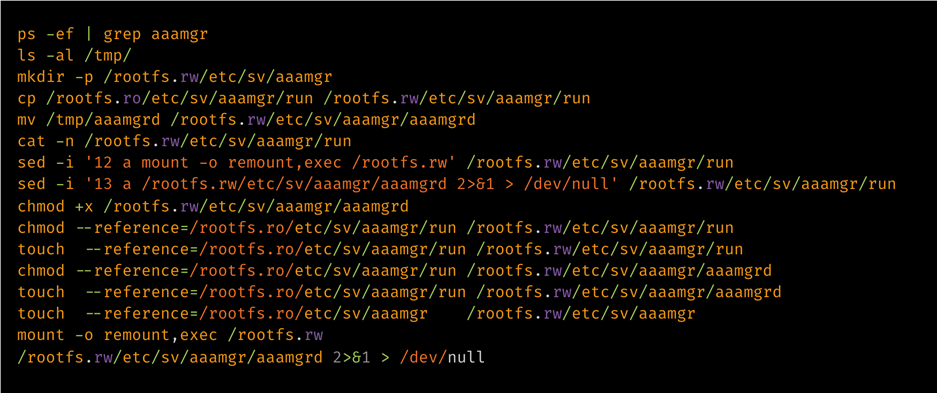
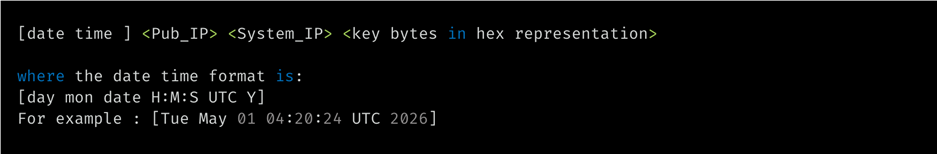
Talos has identified UAT-11473, a highly sophisticated APT, who exploited CVE-2026-20127, an authentication bypass vulnerability in Cisco SD-WAN Catalyst Controller instances to bypass authentication and gain unauthorized access to affected systems to deploy KeyDrift.
Excerpt only, shown with attribution. This content belongs to the original publisher and has not been independently verified by CyberSecurity.pk.
More images
Related CVEs
Keywords: vulnerabilityexploitedmalwareaptthreat advisorycisco talos web filteringlanding page top storytop storyCVE-2026-20127vulnerability newsCisco Talos Intelligencecybersecurity newssecurity news Pakistan
Reference: Cisco Talos Intelligence — blog.talosintelligence.com ↗