

vulnerability
Blog post
NGINX2Root: Five nginx Flaws, Led by CVE-2026-123007. How to Find, Mitigate, and Patch Now
Source: Qualys Security Blog · Published · Last checked 2 hours ago · 1 min read
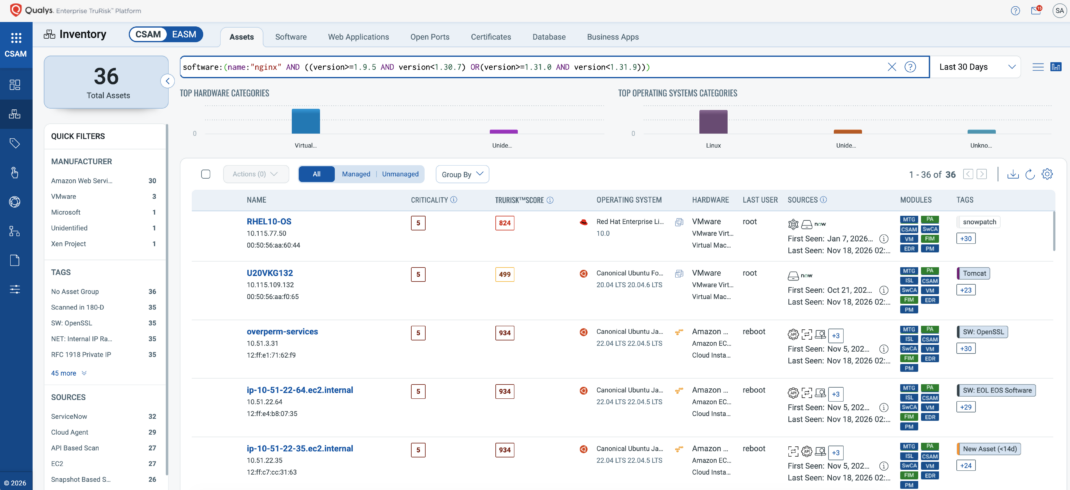
Publisher excerpt From Qualys Security Blog
Executive Summary NGINX2Root is a set of five nginx vulnerabilities disclosed on November 18, 2026. The lead flaw, CVE-2026-123007, is a memory corruption bug in the way nginx handles HTTP/2 connections. F5, which maintains nginx, rates it 9.2 under CVSS v4.0 and 8.1 under CVSS v3.1. An attacker with no credentials can crash nginx worker […]
Excerpt only, shown with attribution. This content belongs to the original publisher and has not been independently verified by CyberSecurity.pk.
Related CVEs
Keywords: patch managementvmdrCVE-2026-123007vulnerabilityvulnerability newsQualys Security Blogcybersecurity newssecurity news Pakistan
Reference: Qualys Security Blog — blog.qualys.com ↗