

general
Blog post
Third-Party JavaScript Is Part of Your Attack Surface: Lessons from a Recent Supply-Chain Attack
Source: Qualys Security Blog · Published · Last checked 20 minutes ago · 1 min read
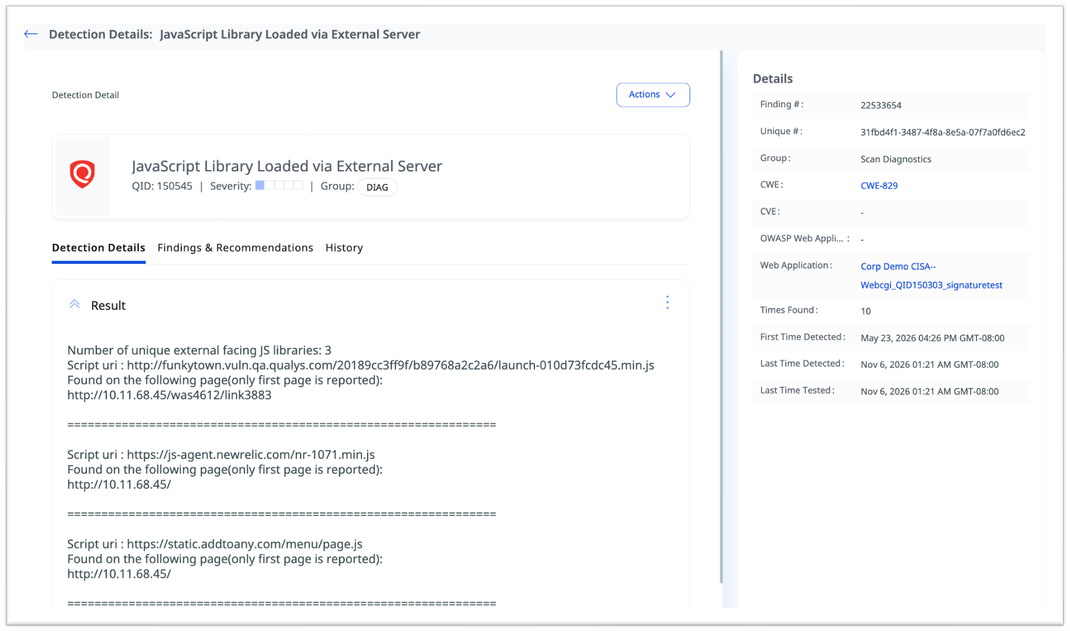
Publisher excerpt From Qualys Security Blog
In a recent incident, visitors to websites run by some of the world’s best-known brands, including news publishers, banks, airlines, and software companies, were served malicious JavaScript. Most of those organizations never deployed bad code. The code came through a script they had deliberately chosen to trust, delivered by a widely used third-party web service. […]
Excerpt only, shown with attribution. This content belongs to the original publisher and has not been independently verified by CyberSecurity.pk.
More images
Keywords: product and techjavascriptgeneralQualys Security Blogcybersecurity newssecurity news Pakistan
Reference: Qualys Security Blog — blog.qualys.com ↗