Independent & educational platformNot a government body. No link or affiliation with any government organisation.Made for learning only. Test only systems you own or are authorised to test.Become a Partner or Sponsor →Full disclaimer
Independent & educational platformNot a government body. No link or affiliation with any government organisation.Made for learning only. Test only systems you own or are authorised to test.Become a Partner or Sponsor →Full disclaimer
Supply chain news
Stories are collected automatically from public feeds, attributed to their original publishers and linked. Editors can remove anything. Always read the original source.
Using compromised credentials, the attackers accessed OpsShield’s update servers and poisoned multiple cPGuard versions.
The post Malicious cPGuard Updates Served in OpsShield Sup...
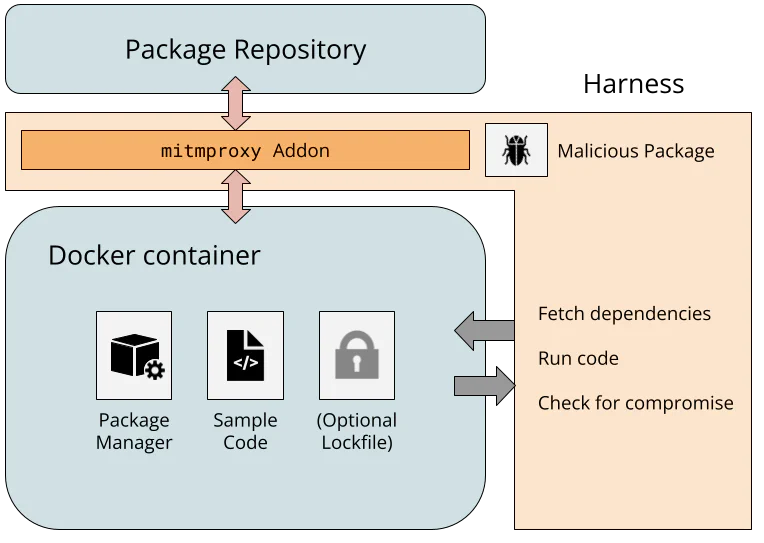
I tested 25 of the most popular package managers to check whether they detect a compromised package repository injecting malicious code into legitimate packages. This code integrit...
What happens when you clear dozens of Trail of Bits engineers’ schedules, pair them with every open-source maintainer they can contact, and unleash the latest frontier models like...
Unit 42 details how threat actors leverage Web3 infrastructure and open-source supply chain attacks to breach enterprise cloud environments
The post Evolution of Web3 in Cloud Sup...
The extension performed host reconnaissance and attempted to create a reverse SSH tunnel.
The post Malicious Claude Code Extension Served in Cursor Supply Chain Attack appeared fi...
Malicious code linked to a website monitoring tool was designed to hijack logged-in Polymarket sessions and siphon user funds.
The post $2 Million+ Drained From Polymarket Traders...
GitHub has announced that it's introducing a new package firewall as a preview to block installation of suspicious npm packages during installation time.
"The firewall inspects bo...
The process that gates nearly every B2B deal is a self-assessment the sender distrusts and the receiver accepts. There is finally a better basis for trust between companies.
The p...
A security research firm reported Monday that it had identified breaches of 42 third-party GitHub repositories in which attackers had deployed payload blobs large enough “to evade...
A recent Shai-Hulud attack shows defenders need real-time visibility into production code and affected services to respond to supply chain compromises.