Independent & educational platformNot a government body. No link or affiliation with any government organisation.Made for learning only. Test only systems you own or are authorised to test.Become a Partner or Sponsor →Full disclaimer
Independent & educational platformNot a government body. No link or affiliation with any government organisation.Made for learning only. Test only systems you own or are authorised to test.Become a Partner or Sponsor →Full disclaimer
Security news
Stories are collected automatically from public feeds, attributed to their original publishers and linked. Editors can remove anything. Always read the original source.
Hackers have been harvesting AI access tokens and have been using AI-assisted offensive tools to automate attacks.
The post AI-Linked Breaches Mount as WorkOS, Northflank, Trigger...
Months after Siemens released fixes for an authentication hole in flow-based programming tool Node-RED, it remains unpatched by many users and attackers are taking advantage of it...
AI-powered malware is “highly likely” to be used in ransomware attacks on Britain’s critical national infrastructure within the next two years.
The head of GCHQ’s National Cyber S...
A Russia-aligned threat actor known as Gorbag has been observed using simple information stealer malware in attacks targeting Ukrainian organizations.
"Active since at least Febru...
The botnet was created and operated for financial gain by Android OEM/ODM Videostrong Technology.
The post Google Dismantles XCPE Botnet of 1.3 Million Android Devices appeared fi...
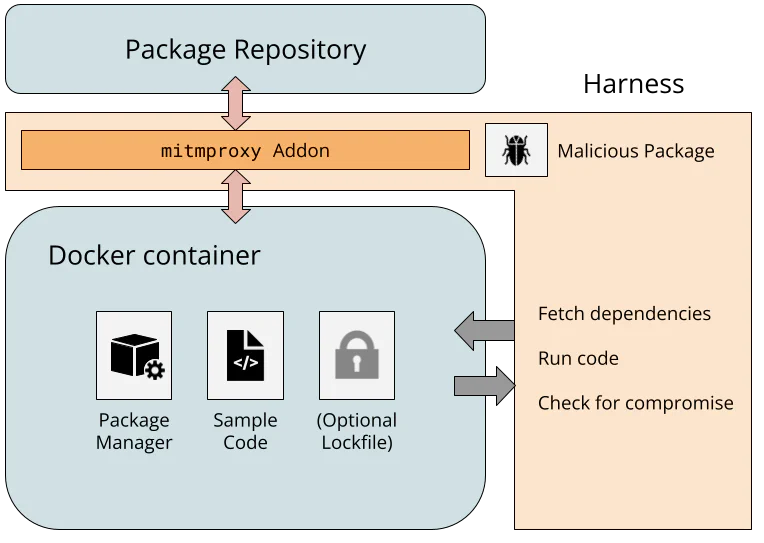
I tested 25 of the most popular package managers to check whether they detect a compromised package repository injecting malicious code into legitimate packages. This code integrit...
Eight compromised eMudhra intermediate CA private keys risk unauthorized TLS signing and MitM interception. Read our analysis and containment guide.
The post EMudhra Intermediate...
An investigation into a threat actor bypassing AI safety controls to coordinate credential theft, VoIP fraud planning, and database exfiltration.
The post “Next Exploit Opportunit...
Our analysis an AI-powered espionage campaign targeting government Linux infrastructure with custom malware, web shells, and advanced credential theft.
The post AI-Powered Espiona...
We investigated an intrusion where attackers exploited CVE-2024-47575 to target 500+ firewalls and deploy PEERSTITCH, a memory-resident ARM64 malware.
The post Unit 42 Uncovers PE...
Analysis of Blinder Tunnel, an Iran-nexus campaign using fake Dubai Airports recruitment lures and GitHub C2 malware to target critical infrastructure.
The post Blinder Tunnel Cam...
We introduce OperTraitor, a tool to audit privileges of Kubernetes operators, identify excessive RBAC risks, and secure non-human identities.
The post OperTraitors: How Kubernetes...