Independent & educational platformNot a government body. No link or affiliation with any government organisation.Made for learning only. Test only systems you own or are authorised to test.Become a Partner or Sponsor →Full disclaimer
Independent & educational platformNot a government body. No link or affiliation with any government organisation.Made for learning only. Test only systems you own or are authorised to test.Become a Partner or Sponsor →Full disclaimer
Security news
Stories are collected automatically from public feeds, attributed to their original publishers and linked. Editors can remove anything. Always read the original source.
SonicWall has warned of two vulnerabilities impacting end-of-life Global Management System (GMS) systems that it said will not be patched.
Details of the security flaws, which aff...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a security flaw in WordPress Core to the Known Exploited Vulnerabilities (KEV) catalog, citing evidence o...
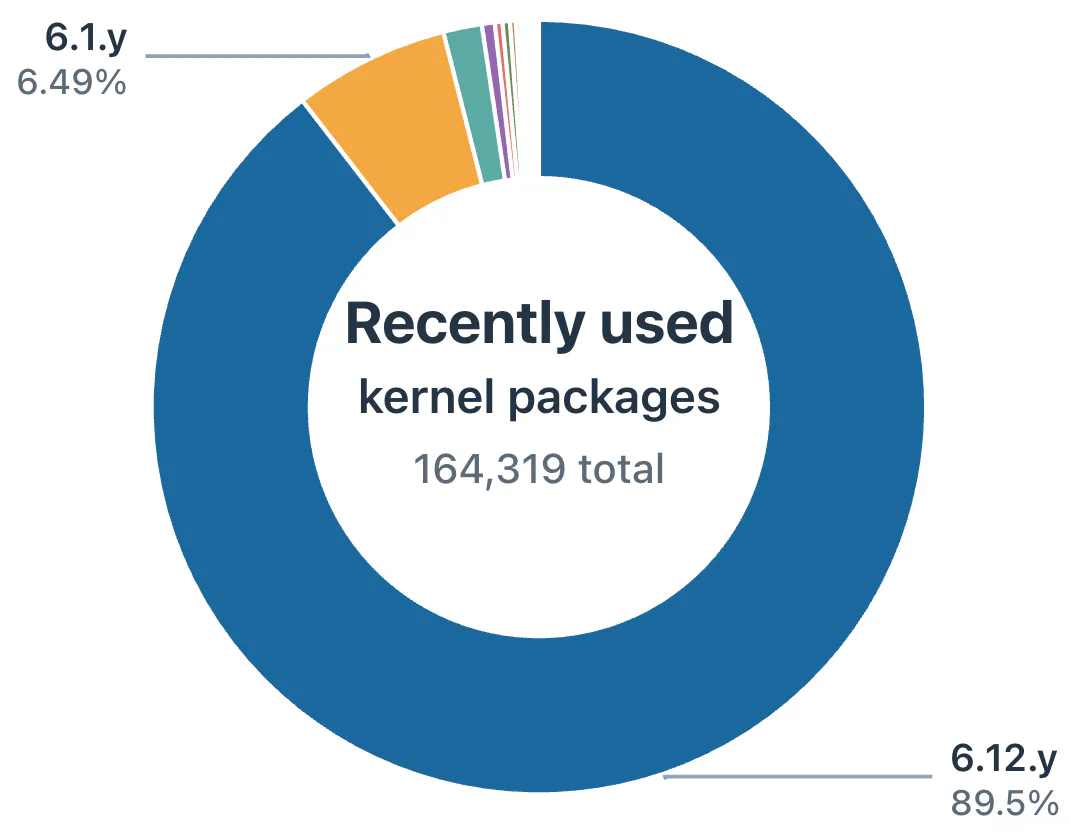
Stable Linux releases lack existing security fixes because backporting them is time-consuming and often thankless work. We’re using Codex to reduce the backporting process time fro...
A maximum-severity security flaw impacting Siemens SIMATIC IoT2050 Advanced devices has come under active exploitation, VulnCheck has revealed.
The vulnerability, tracked as CVE-2...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added two security flaws impacting Ivanti Connect Secure (ICS) to its Known Exploited Vulnerabilities (KE...
Threat actors have been observed attempting to exploit a high-severity security flaw in WordPress Core shortly after patches were released.
The vulnerability, which does not have...
Drupal has warned that threat actors are exploiting a "highly critical" security flaw in its Commerce Core component.
The vulnerability, tracked as CVE-2026-118539 (CVSS score: N/...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added two security flaws impacting Cisco and GitLab software to its Known Exploited Vulnerabilities (KE...
More evidence has emerged that attackers are turning to vulnerabilities rather than phishing as a means for breaking into corporate systems.
Incident response firm LevelBlue’s Q3...
Cisco has released patches to address a high-severity security flaw in Secure Firewall Adaptive Security Appliance (ASA) Software and Secure Firewall Threat Defense (FTD) Software...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a security flaw impacting Broadcom VMware ESX to its Known Exploited Vulnerabilities (KEV) catal...
Adobe has released patches to address multiple critical security flaws in Campaign Classic that, if successfully exploited, could result in arbitrary code execution, security featu...