Independent & educational platformNot a government body. No link or affiliation with any government organisation.Made for learning only. Test only systems you own or are authorised to test.Become a Partner or Sponsor →Full disclaimer
Independent & educational platformNot a government body. No link or affiliation with any government organisation.Made for learning only. Test only systems you own or are authorised to test.Become a Partner or Sponsor →Full disclaimer
Security news
Stories are collected automatically from public feeds, attributed to their original publishers and linked. Editors can remove anything. Always read the original source.
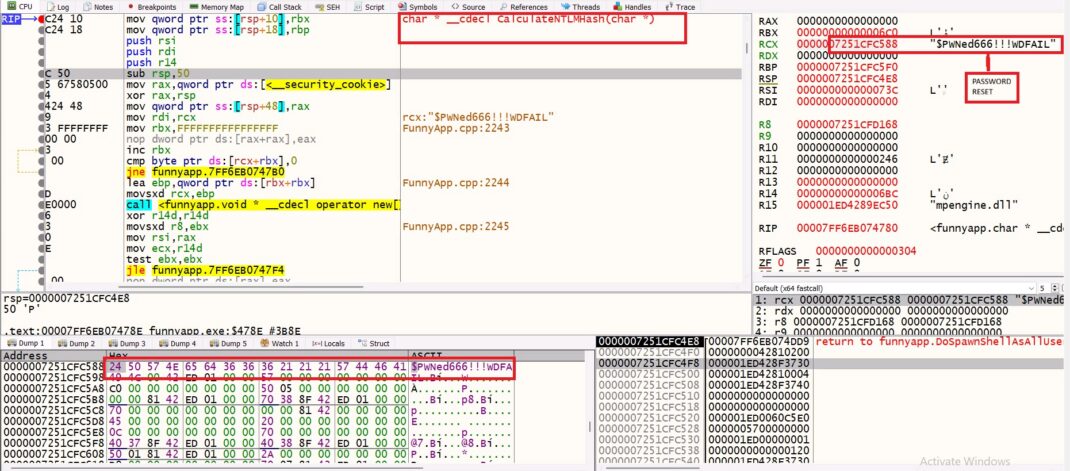
Executive Summary BlueHammer (CVE-2026-33825) is an eight-stage local privilege-escalation chain targeting the Windows Defender Antimalware Platform before 4.18.26030.3011. It does...
Key Points Introduction Over the past two months, we have been tracking a campaign that abuses the popularity of AI tools such as ChatGPT and Claude to spread a custom malware chai...
For the latest discoveries in cyber research for the week of 26th October, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Japanese cloud hosting provide...
Key Points Introduction Infostealers commonly target browser passwords, session cookies, and cryptocurrency wallets. This malware combines those established capabilities with dedic...
Heads up: the first 7 mins is a bit quiet until we worked out the external mic was misbehaving - sorry! But get through that and have a listen to Scott's experiences with how Repor...
The extension performed host reconnaissance and attempted to create a reverse SSH tunnel.
The post Malicious Claude Code Extension Served in Cursor Supply Chain Attack appeared fi...
A malicious version of Anthropic’s Claude Code extension distributed through the Cursor marketplace attempted to install a persistent Secure Shell (SSH) backdoor on developers’ mac...
Just a couple of weeks after a cyberattack on French supermarket refrigeration systems resulted in spoiled food, and even some fires, retailers in Belgium, Ireland, Sweden, Finland...
Cybersecurity researchers have discovered a new Windows infostealer malware called VOLTA-AUTODOXER (aka VOLTA) that makes use of a large language model (LLM) to rank a victim's sto...
Cybersecurity researchers have disclosed details of what has been described as a "highly sophisticated infection chain" targeting government organizations in Asia.
The activity, d...
In May 2017, the WannaCry cryptoworm spread across the internet, compromising more than 200,000 computers in at least 100 countries. The National Audit Office called it the largest...