Independent & educational platformNot a government body. No link or affiliation with any government organisation.Made for learning only. Test only systems you own or are authorised to test.Become a Partner or Sponsor →Full disclaimer
Independent & educational platformNot a government body. No link or affiliation with any government organisation.Made for learning only. Test only systems you own or are authorised to test.Become a Partner or Sponsor →Full disclaimer
Security news
Stories are collected automatically from public feeds, attributed to their original publishers and linked. Editors can remove anything. Always read the original source.
A flaw in APT, the package manager for Debian and Ubuntu, allows an attacker who can modify package downloads to swap a checked package for their own.
The attacker's code then run...
SonicWall has warned of two vulnerabilities impacting end-of-life Global Management System (GMS) systems that it said will not be patched.
Details of the security flaws, which aff...
Cybersecurity researchers have disclosed details of an OpenAI Codex jailbreak bundle that's designed to modify an artificial intelligence (AI) agent's trusted instructions to inser...
A single container image that brings Vulnerability Management and Policy Audit to every Kubernetes node, on immutable and mutable Linux alike, deployed the way your container workl...
Personal AI agents have changed how users interact with the web, blurring the lines between automated and human traffic. Learn how Cloudflare gives site owners visibility and contr...
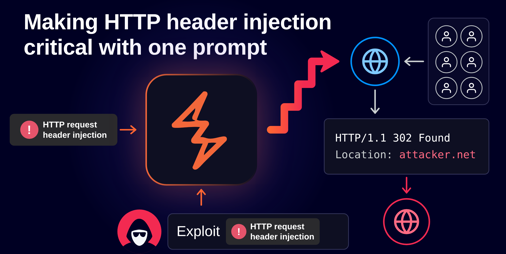
You can now escalate HTTP header injection to a CRLF-Powered Desync and exploit it to serve random users a redirect to your collaborator, in a single prompt. We’ve just introduced...
Organizations may not be ready for completely autonomous communication processes, but there are places where automating information updates would alleviate pressure.
The Russia-linked threat actor known as APT29 is said to be behind a large-scale watering hole campaign targeting iOS and Android users through compromised websites, fake domains,...
Sysdig’s platform uses runtime visibility to track AI agent actions and block risky behavior before it reaches production systems.
The post Sysdig Adds Runtime Security and Govern...
An authentication bypass and a command injection flaw can be chained for root access on Barracuda’s Email Security Gateway appliances.
The post Barracuda ESG Authentication Bypass...
The company will invest in agentic data security capabilities and expand its go-to-market organization.
The post Agentic Data Security Firm Sentra Raises $150 Million appeared fir...
Users looking for cracked commercial software, free games, plugins, and unofficial utilities could be signing up for more than a free download. Microsoft has observed an evolving c...