Independent & educational platformNot a government body. No link or affiliation with any government organisation.Made for learning only. Test only systems you own or are authorised to test.Become a Partner or Sponsor →Full disclaimer
Independent & educational platformNot a government body. No link or affiliation with any government organisation.Made for learning only. Test only systems you own or are authorised to test.Become a Partner or Sponsor →Full disclaimer
Security news
Stories are collected automatically from public feeds, attributed to their original publishers and linked. Editors can remove anything. Always read the original source.
An authentication bypass and a command injection flaw can be chained for root access on Barracuda’s Email Security Gateway appliances.
The post Barracuda ESG Authentication Bypass...
The browser update resolves dozens of memory safety bugs and incorrect/missing authorization issues.
The post Chrome 157 Rolls Out With 213 Security Fixes, Seven Rated Critical ap...
A $300,000 award went to a pre-launch flaw that exposed conversations and tokens on internal Muse test VMs used by Meta staff.
The post Meta Shares Top Muse Bug Bounty Findings as...
Zero Wire on Cloudflare Radar pairs plain-language briefings with global attack telemetry and remediation steps. Triage critical CVEs faster and decide how to protect your infrastr...
The most severe is a critical flaw in Framework leading to remote code execution without user interaction.
The post Android’s November 2026 Updates Patch Over 200 Vulnerabilities...
Multiple attacks from the same IP address attempted to deploy various payloads, including a Linux bot and webshells.
The post Critical Node-RED Flaw Exploited in Attacks appeared...
Ransomware operators including Spikey Scorpius (aka Qilin) and Tarnished Scorpius (aka Inc) are exploiting PAN-OS vulnerability CVE-2026-0257.
The post Active Exploitation of May...
Unit 42 is aware of possible 0-day activity against NetScaler devices. Citrix reports CVE-2026-88771, CVE-2026-88772 have been exploited in the wild.
The post Threat Brief: NetSc...
We introduce OperTraitor, a tool to audit privileges of Kubernetes operators, identify excessive RBAC risks, and secure non-human identities.
The post OperTraitors: How Kubernetes...
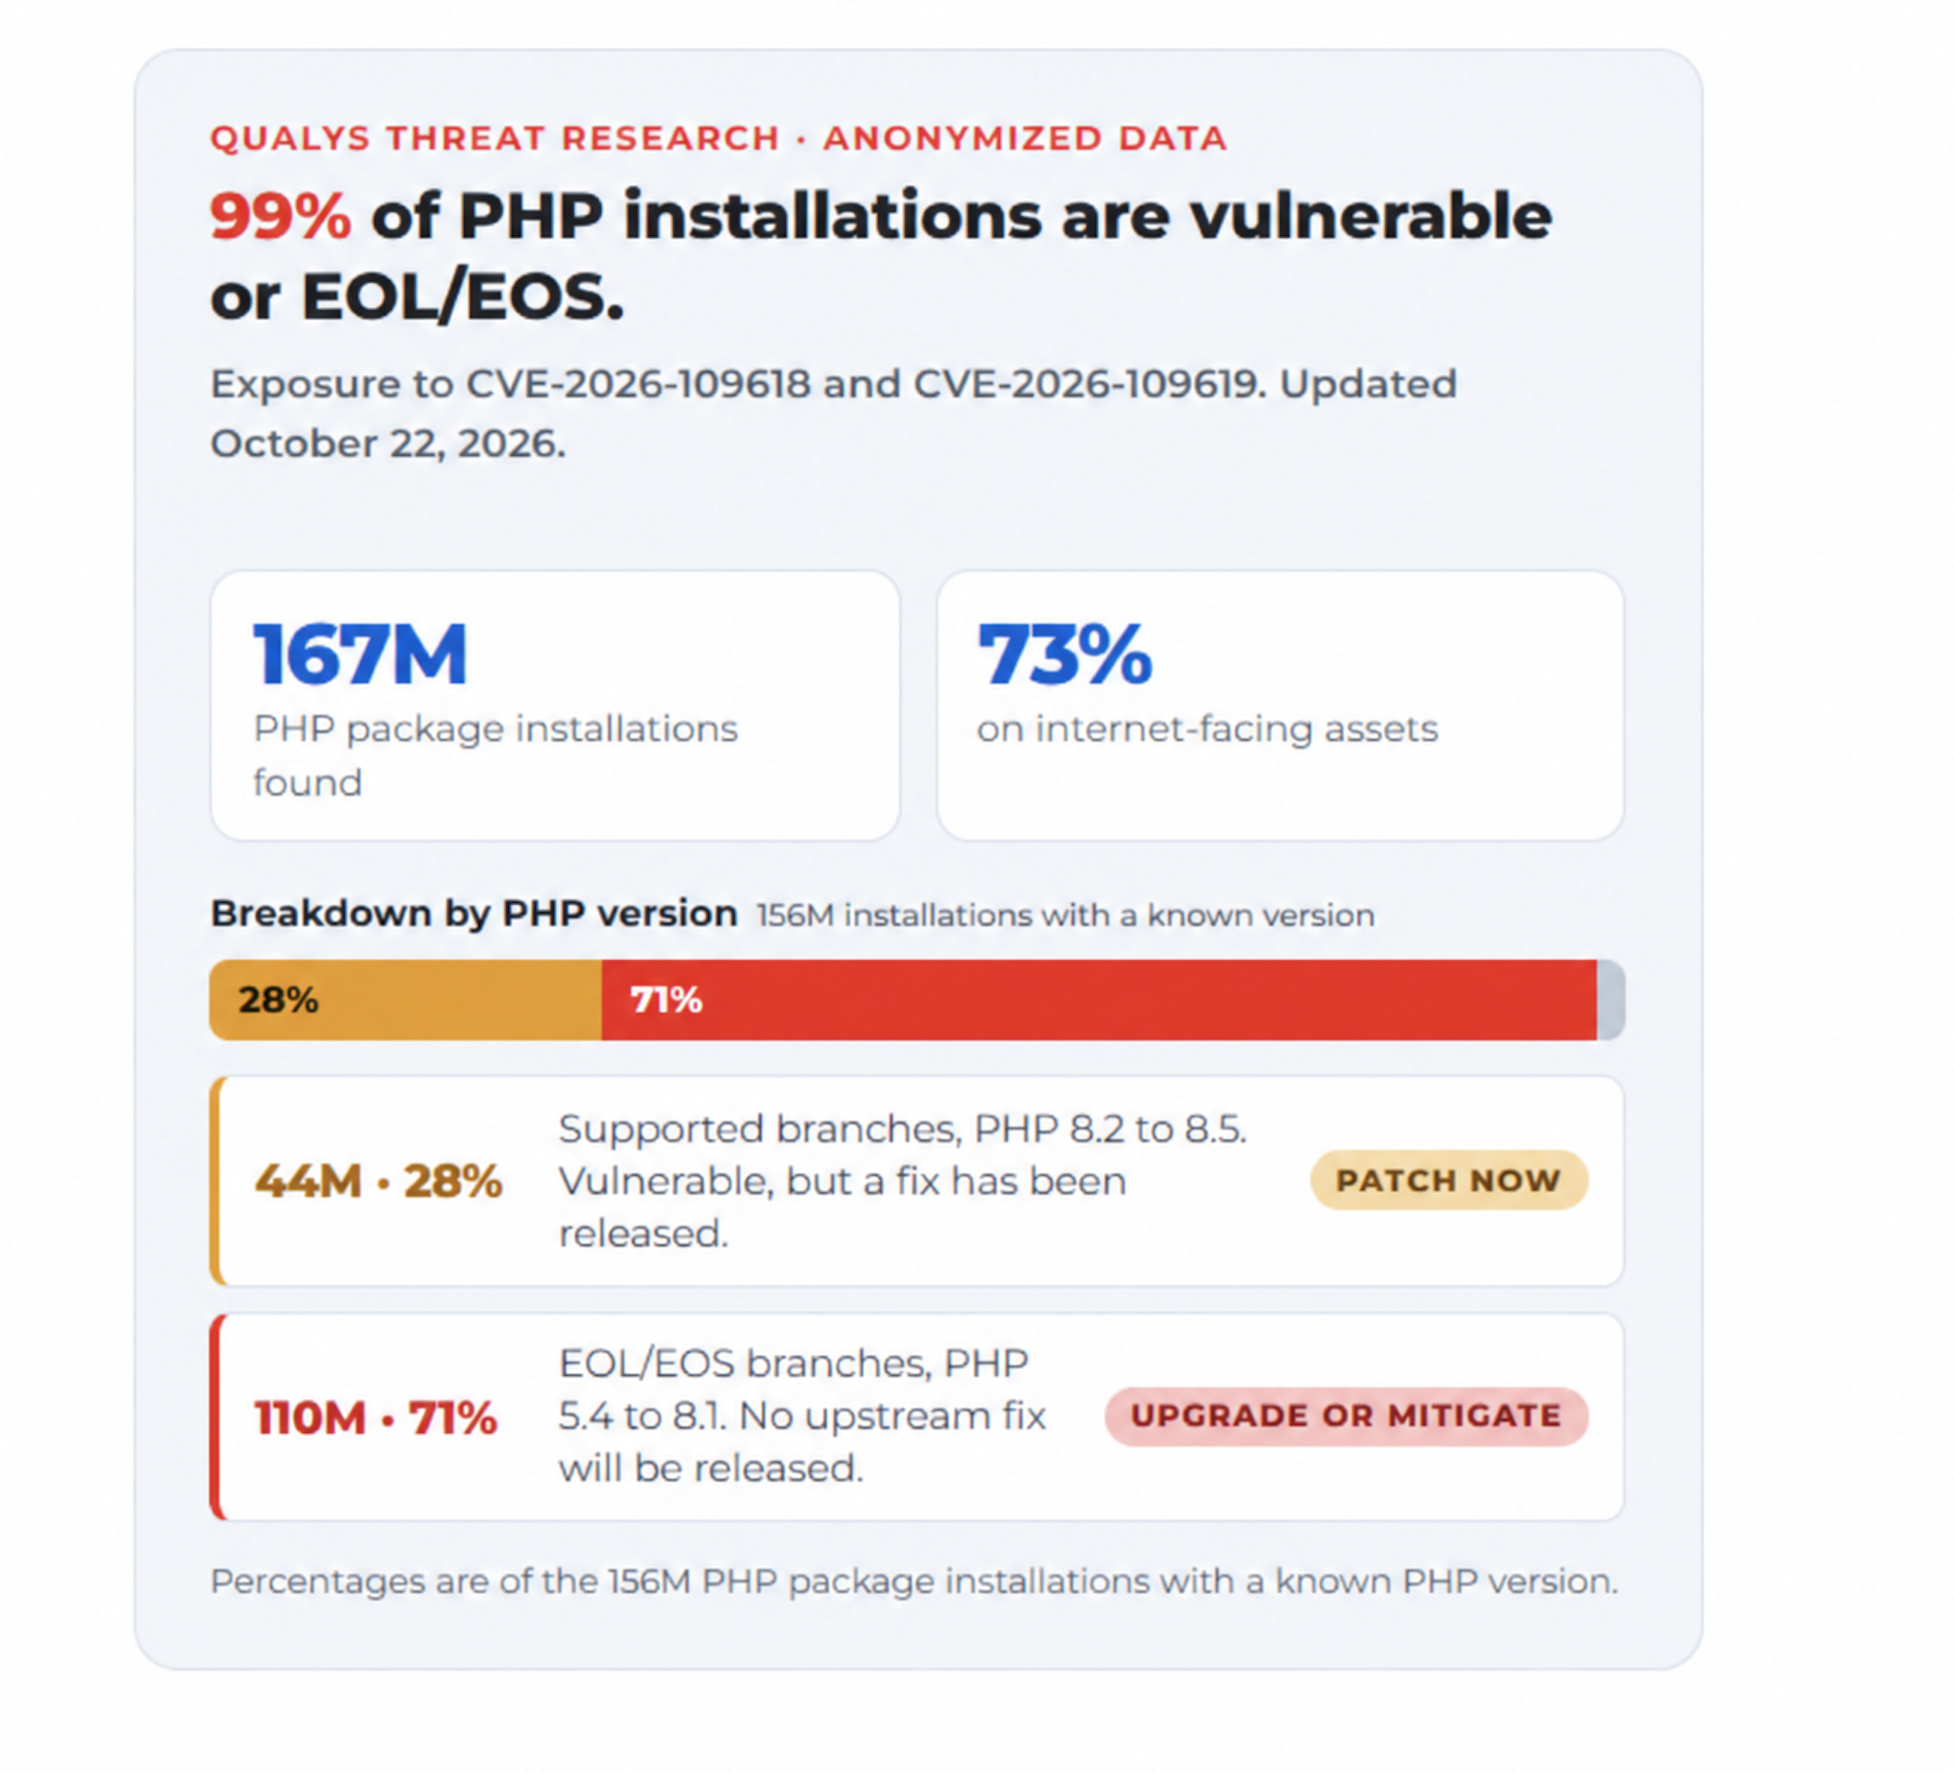
Executive Summary PHP2Shell’s fix is to update PHP, but patching at scale is slow. Only 199,000 of 156 million PHP installations were patched in the first 12 hours after disclosure...
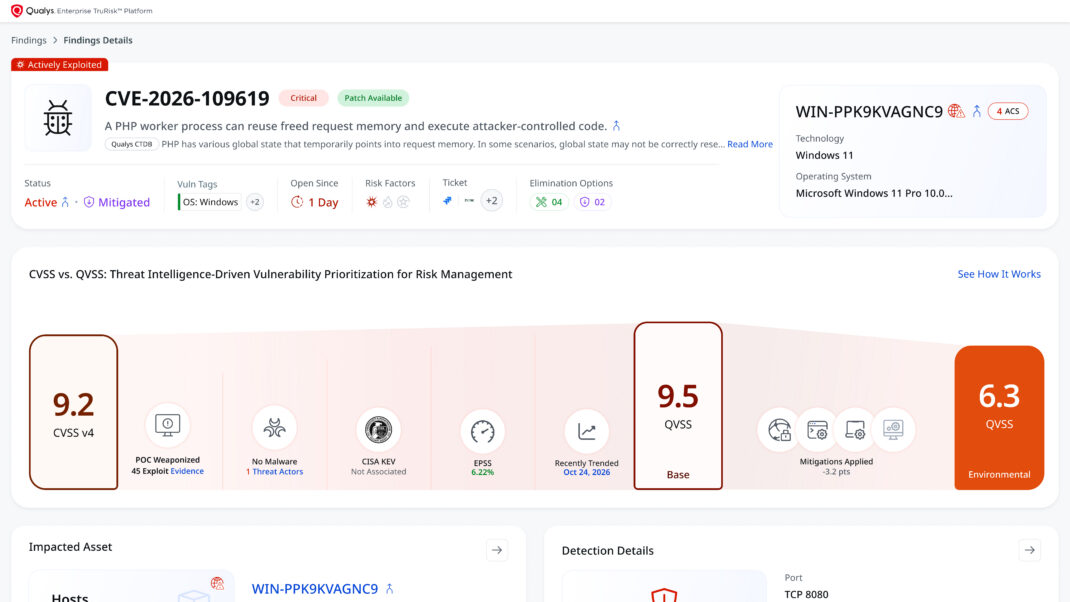
Executive Summary PHP2Shell refers to two critical vulnerabilities (CVE-2026-109618 and CVE-2026-109619), each with a CVSS v4.0 score of 9.2, that can allow unauthenticated remote...
CVE-2026-109618 and CVE-2026-109619 are Critical vulnerabilities in PHP, a scripting language used globally for web servers and CMS systems.
The post Threat Brief: Critical Vulner...